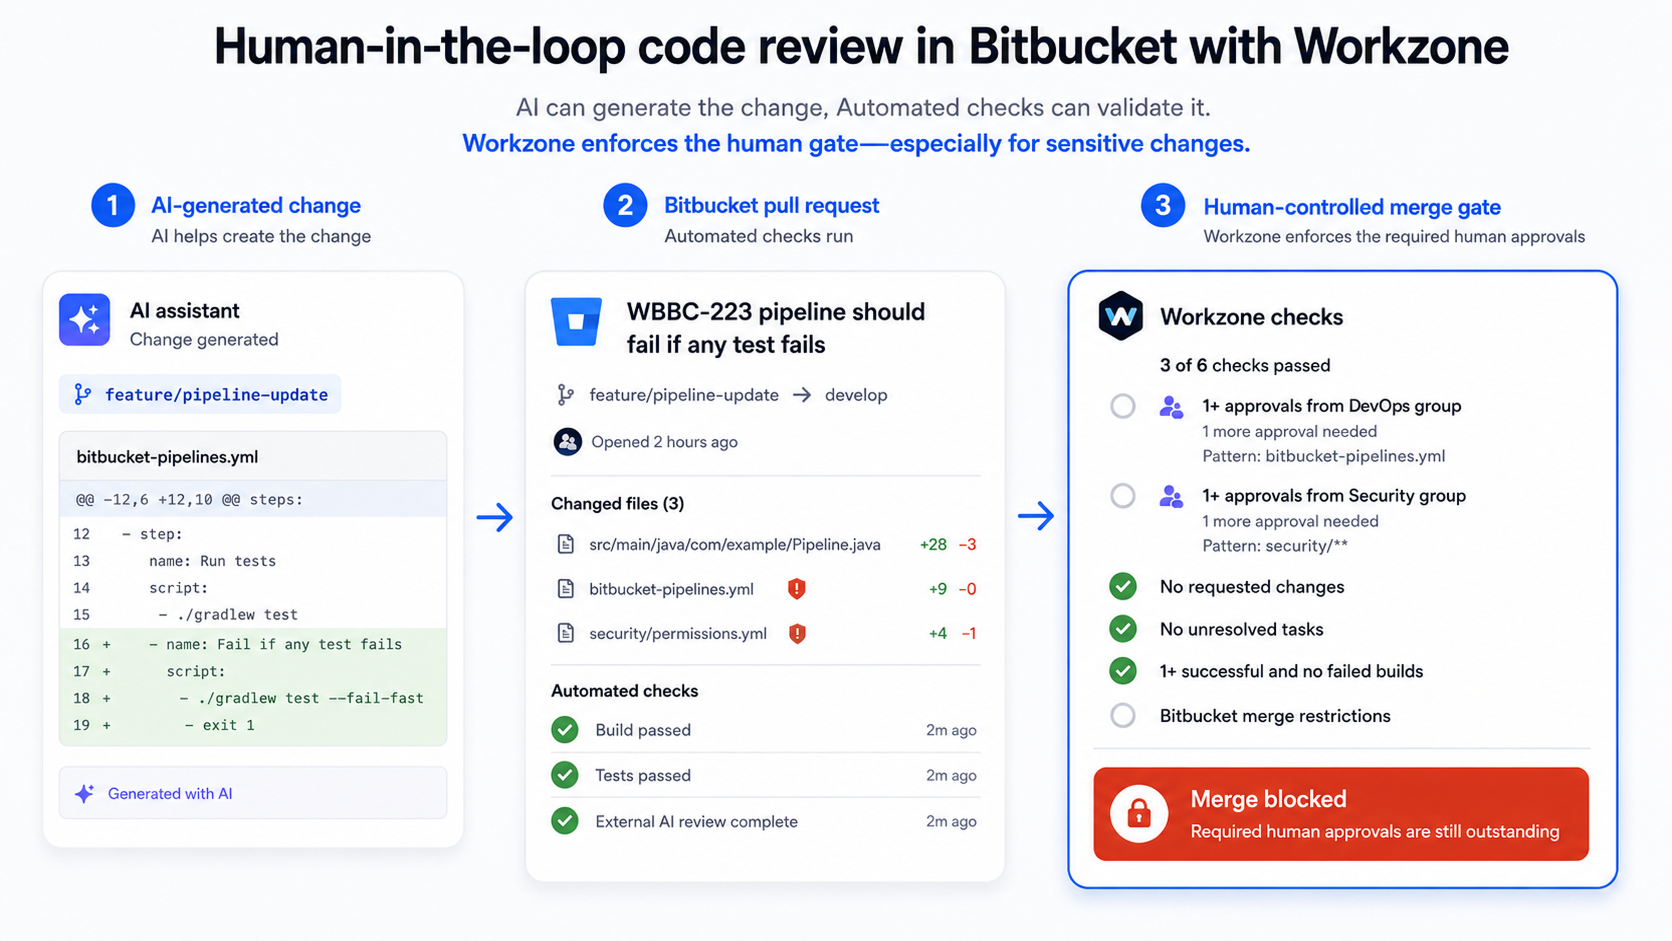
Protecting Critical Code in Bitbucket in the Age of AI
AI-assisted development can dramatically increase the amount of code a team produces. For teams adopting coding agents, the challenge is increasingly how to protect critical code in Bitbucket without turning every pull request into a bottleneck.
The answer is not to manually scrutinise every AI-generated line equally. It is to review according to risk: automate the checks machines can perform reliably, while making human approval mandatory for the files, branches and decisions where human judgment is genuinely important.
In other words, the goal is not simply to keep a human somewhere in the loop. It is to make sure the right human remains a required part of the loop when the consequences of getting a change wrong are significant.
Note: This article focuses primarily on Bitbucket Cloud. Workzone is also available for Bitbucket Data Center, but Bitbucket’s native review and merge capabilities differ between the two platforms.
Key Takeaways
- AI can increase development throughput, making scalable code review and clearly defined ownership more important.
- Low-risk and high-risk changes should not necessarily require the same level of human review.
- Bitbucket Cloud CODEOWNERS can assign reviewers based on changed files, while Bitbucket Premium can enforce general approval-related merge checks.
- Workzone can tie specific branches and file/module patterns to reviewer users, groups and explicit approval quotas.
- Automated tests, security scanning and AI review should complement accountable human review, not replace it where human judgment matters.
AI Has Changed the Code Review Bottleneck
The simple story about AI-assisted software development is that developers can now write code faster.
That is true, but it misses a more important change: producing code is becoming easier than understanding and verifying it.
An AI agent can generate a feature, refactor a module, update tests and prepare a pull request in a fraction of the time the same work may previously have taken. The resulting code can look polished, follow familiar patterns and even pass its tests.
That creates a different kind of risk.
Obviously bad code is often relatively easy to detect. More difficult is plausible code: code that looks correct, compiles successfully and passes expected tests while subtly changing behaviour, introducing an edge case or making an assumption the team never intended.
As Addy Osmani writes in his article on agentic code review, “Writing got cheap, understanding didn’t.”
For Bitbucket teams, much of that verification pressure eventually arrives at the pull request.
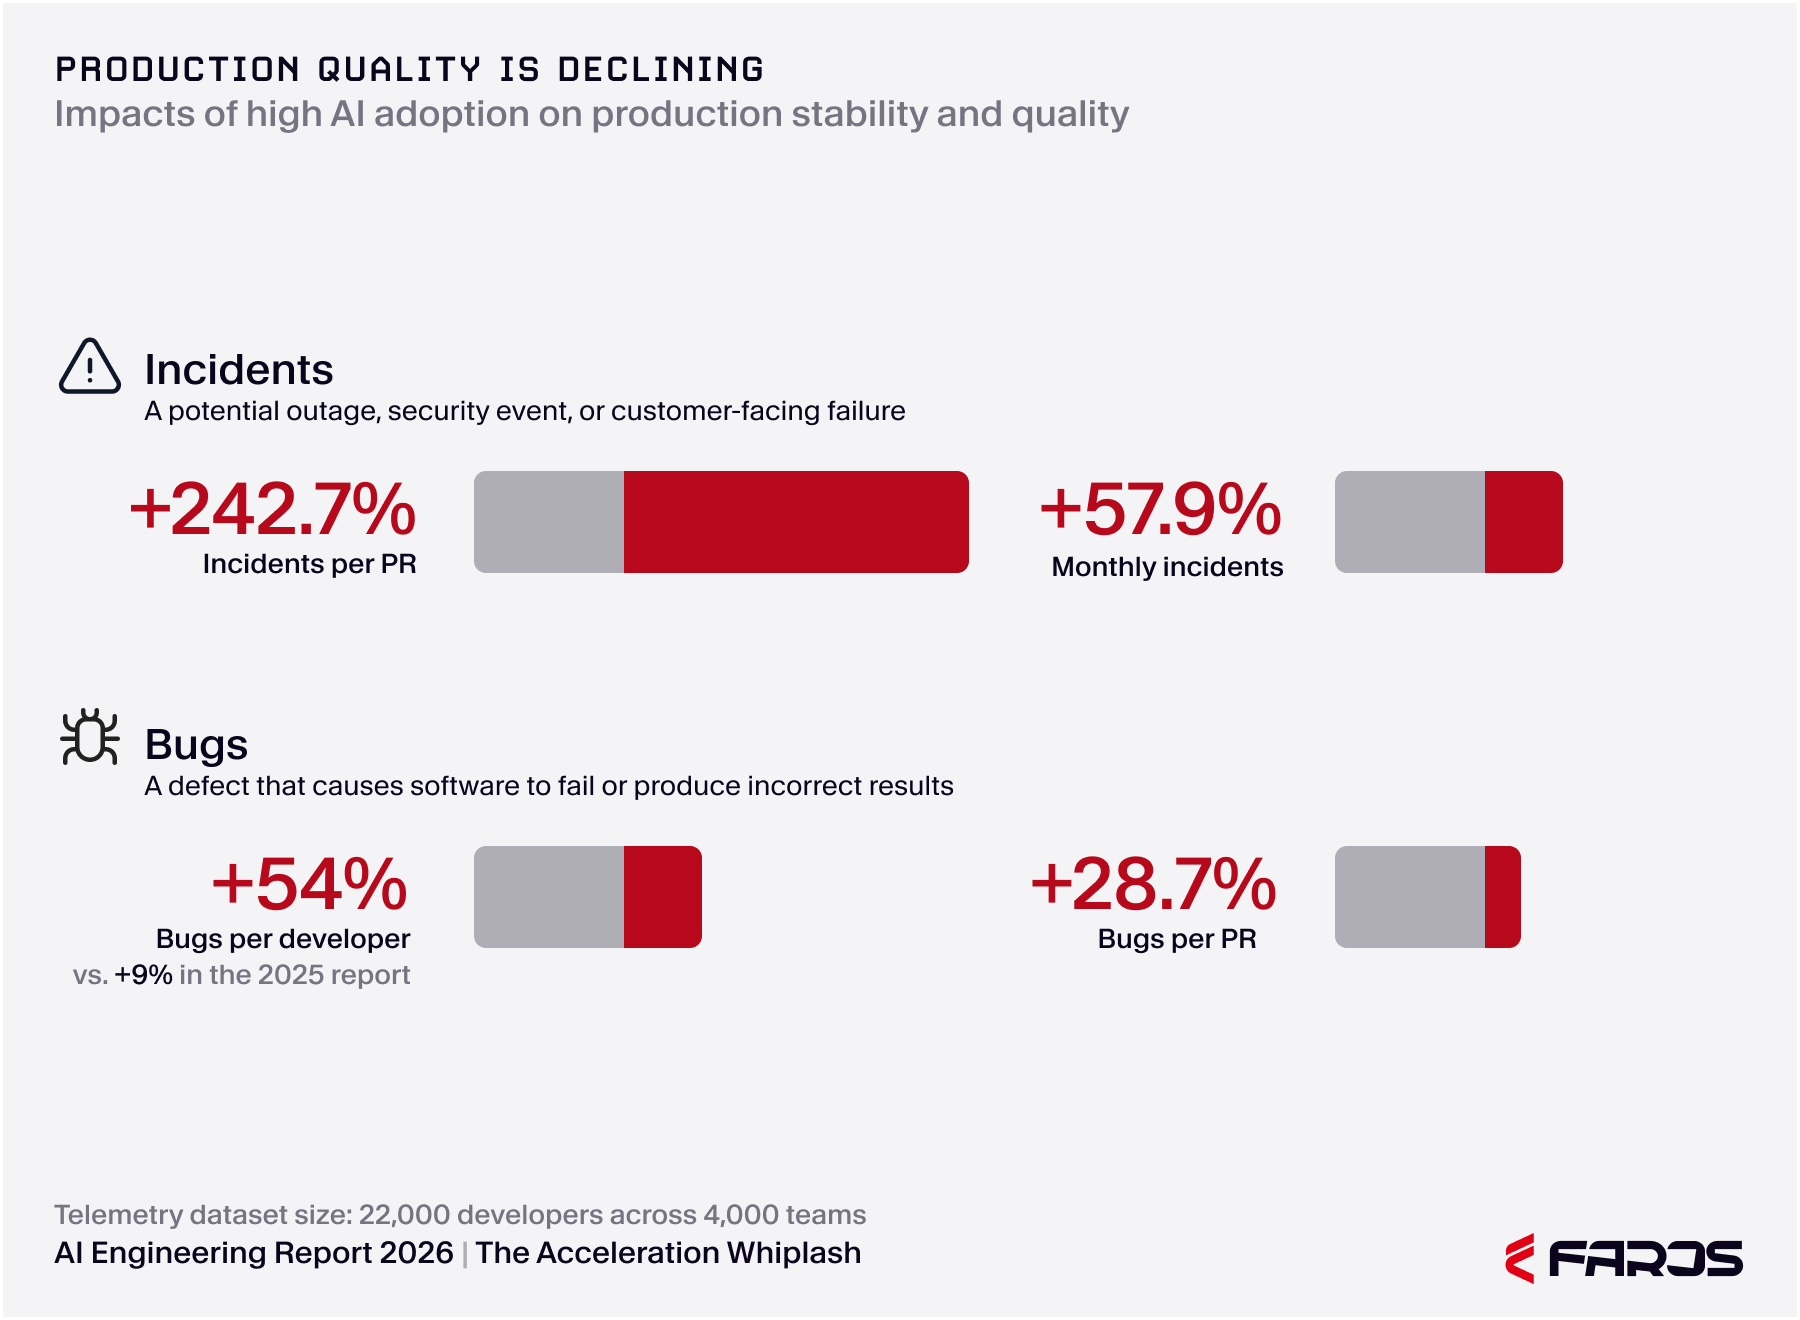
Research is also beginning to show what can happen when AI-assisted development increases code output faster than engineering systems adapt. Faros AI’s 2026 Acceleration Whiplash report, based on two years of telemetry from 22,000 developers across more than 4,000 teams, reports larger pull requests, longer review times, more incidents per pull request and substantially greater code churn alongside higher AI adoption.
DORA’s 2025 State of AI-assisted Software Development provides a useful broader perspective: AI appears to act as an amplifier of the engineering system around it. Strong delivery practices can benefit from increased capability, while weaknesses in the underlying process can also be magnified.
The practical lesson is not that AI-generated code is inherently unsafe.
It is that faster code generation increases the importance of having a review system that knows where human attention matters most.
AI Review Is Useful, but It Is Not Ownership
AI can also help with the review problem.
AI code reviewers can identify suspicious logic, missing tests, security concerns, inconsistencies and other potential problems before a human reviewer spends time on a pull request. Different automated reviewers may also detect different classes of issues.
That makes AI an increasingly useful sensor in the review process.
But a sensor is not the same thing as an accountable owner.
An AI reviewer can flag a potential problem or conclude that a change looks reasonable. It cannot take organisational responsibility for a production incident, understand every customer commitment or make an accountable decision about whether a particular business risk should be accepted.
That distinction matters.
AI can scale checking. Human reviewers still own judgment.
The challenge is therefore deciding where that human judgment needs to remain mandatory.
How to Protect Critical Code in Bitbucket Based on Blast Radius
Not every file in a repository carries the same risk.
Changing a documentation page is not equivalent to changing authentication logic. Updating UI copy is not equivalent to modifying a deployment pipeline. A low-risk refactor is not necessarily comparable to a change affecting customer data, infrastructure, billing or a regulated workflow.
A practical way to protect critical code in Bitbucket is to make review depth follow the blast radius of getting the change wrong.
| Changed area | Typical risk | Example review policy |
|---|---|---|
docs/** | Low | Automated checks and lightweight review |
src/ui/** | Moderate | Review from the responsible UI team |
src/auth/** | High | Required approval from responsible security/backend reviewers |
infrastructure/** | High | Platform or release-team approval plus successful build |
db/migrations/** | High | Required approval from the appropriate backend/data owner |
These are only examples. Every organisation will have different critical files and different ownership structures.
The important question is:
Which parts of your repository should never reach a protected branch without approval from the people accountable for them?
- CI/CD pipeline configuration
- infrastructure-as-code
- deployment scripts
- authentication and authorisation logic
- security and permission configuration
- database migrations
- billing, payment or licensing logic
- regulated workflow code
- critical configuration used by customers
AI can still propose changes to these files. A developer can still commit them.
The control point is whether those changes can actually be merged without satisfying the appropriate review requirements.
Workzone Turns Code Ownership Into an Enforceable Review Rule
Workzone for Bitbucket allows pull request reviewer rules to reflect the part of the codebase being changed.
Its reviewer and approval configuration can use branch patterns, file or module patterns, individual reviewers, reviewer groups and approval quotas.
For example, a team might require changes under src/ui/** to receive approval from a UI reviewer while changes to an authentication module require approval from the appropriate backend or security group.
For particularly sensitive paths, the configured reviewers and approval quota become part of the Workzone merge requirements.
This turns:
Someone from this team should probably review changes here.
into:
This change cannot satisfy the configured merge requirements until the appropriate review condition has been met.
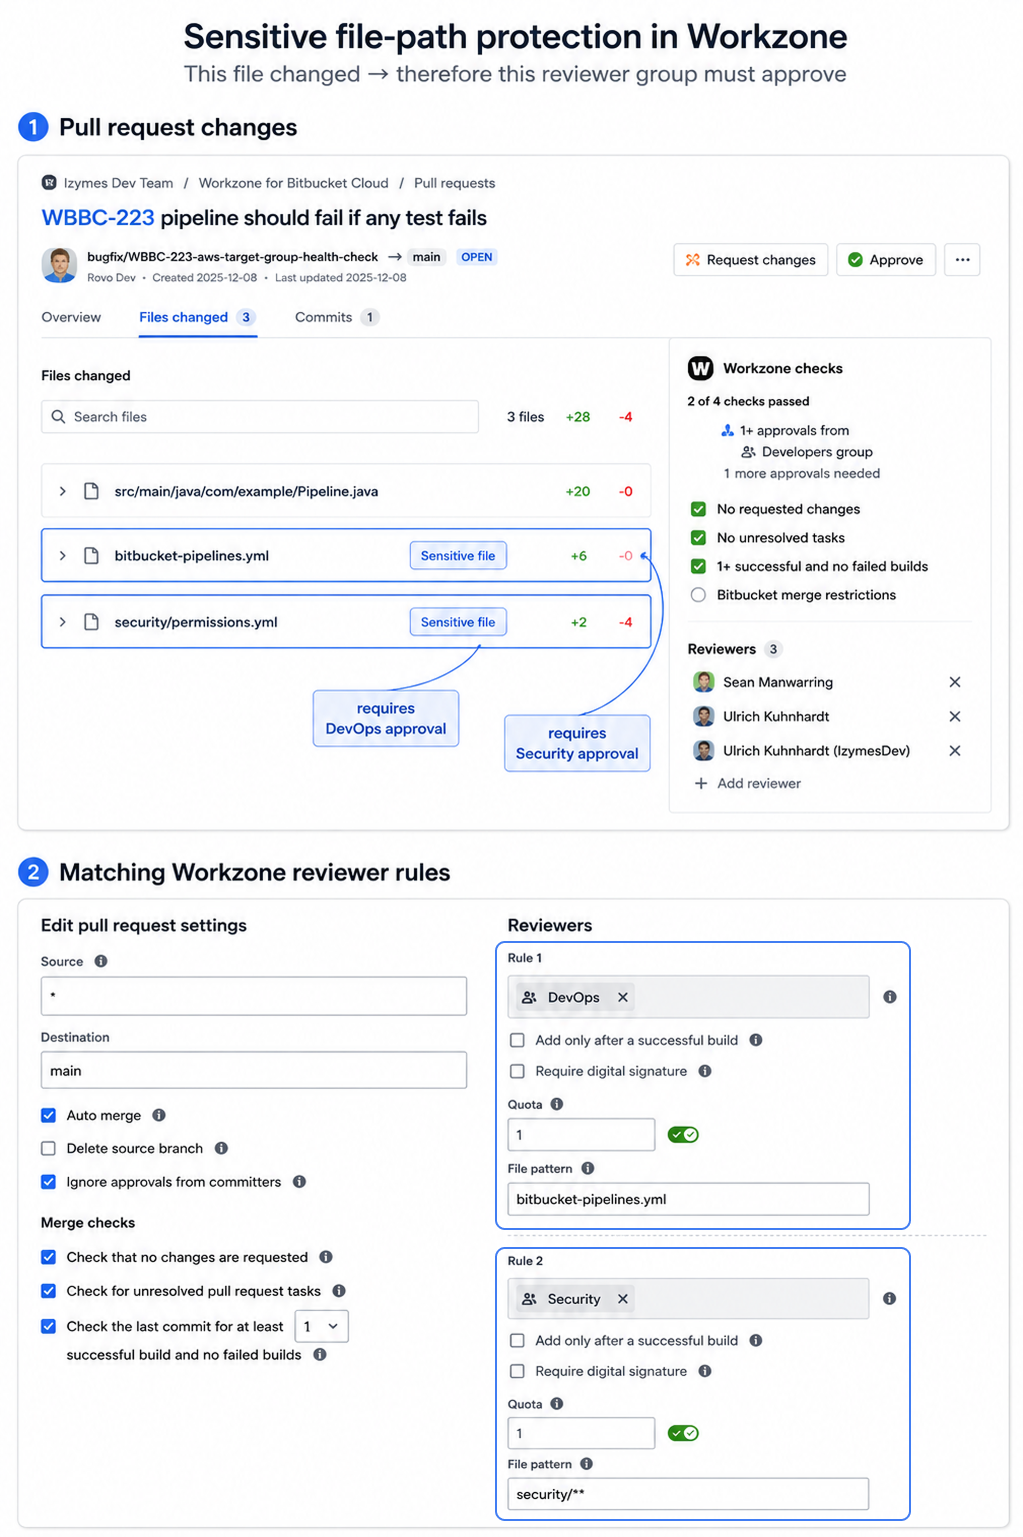
That distinction becomes increasingly valuable when AI-assisted pull requests become larger or more frequent. The workflow does not depend on someone manually noticing that a sensitive file happens to be buried inside a large diff.
Independent Review Matters When Authorship Gets Messy
AI-assisted development can also make authorship less straightforward.
A developer may generate the original change with an AI agent. Another engineer may modify it. Someone might approve the pull request and then subsequently add a commit.
For many teams, that is not a significant problem.
For workflows that specifically require independent review, however, an important question appears:
Should the approval of someone who contributed to the change still satisfy the independent approval requirement?
Workzone can be configured to ignore approvals from committers when calculating its approval quota. The approval itself remains visible in Bitbucket, but if the reviewer has contributed commits to the pull request, their approval does not satisfy the configured Workzone quota.
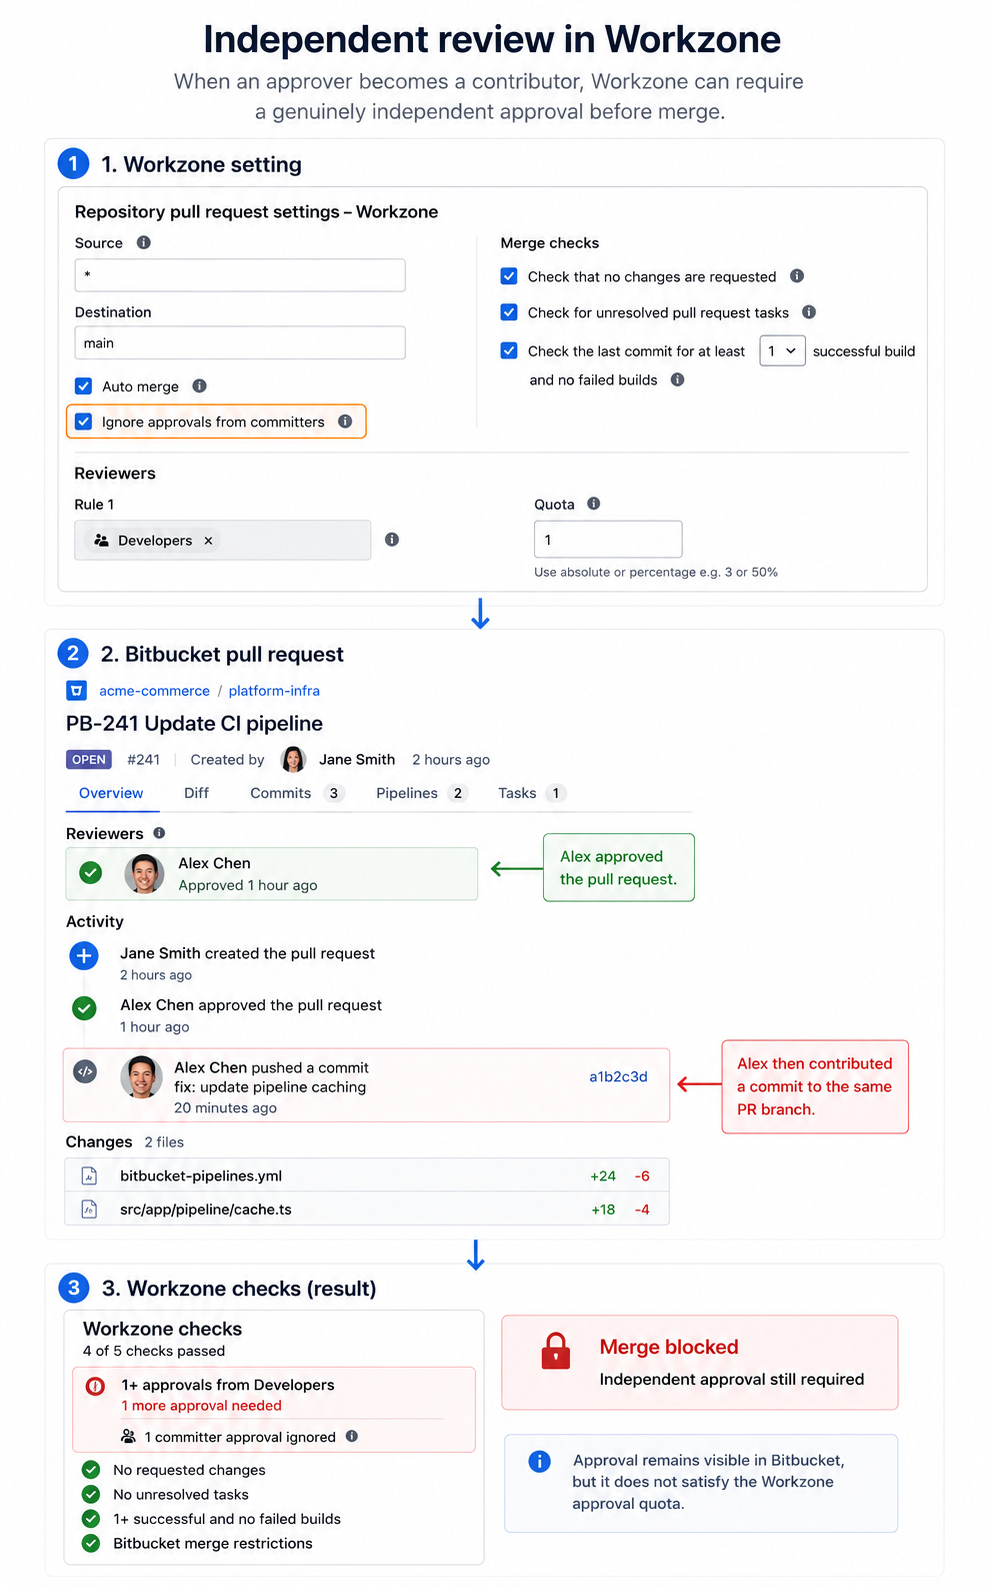
That allows teams to distinguish between an approval and an independent approval.
This distinction can be particularly useful for high-risk or compliance-sensitive development processes.
Automation Should Protect Human Attention, Not Remove Accountability
Keeping humans involved does not mean replacing automation with manual processes.
The opposite is usually more effective.
Linters, automated tests, builds, security scanners, AI review tools and other deterministic checks should handle tasks that machines can perform consistently.
Human attention can then be concentrated on questions that require context and accountability:
- Is this the right change?
- Does it introduce an unacceptable risk?
- Does it fit the architecture?
- Does it affect contractual, security or compliance requirements?
- Is the organisation comfortable putting this change into production?
Workzone branch configurations can combine reviewer requirements with merge checks such as successful builds, unresolved tasks, requested changes and approval requirements.
For workflows requiring stronger evidence of approval, Workzone can also require digitally signed pull request approvals.
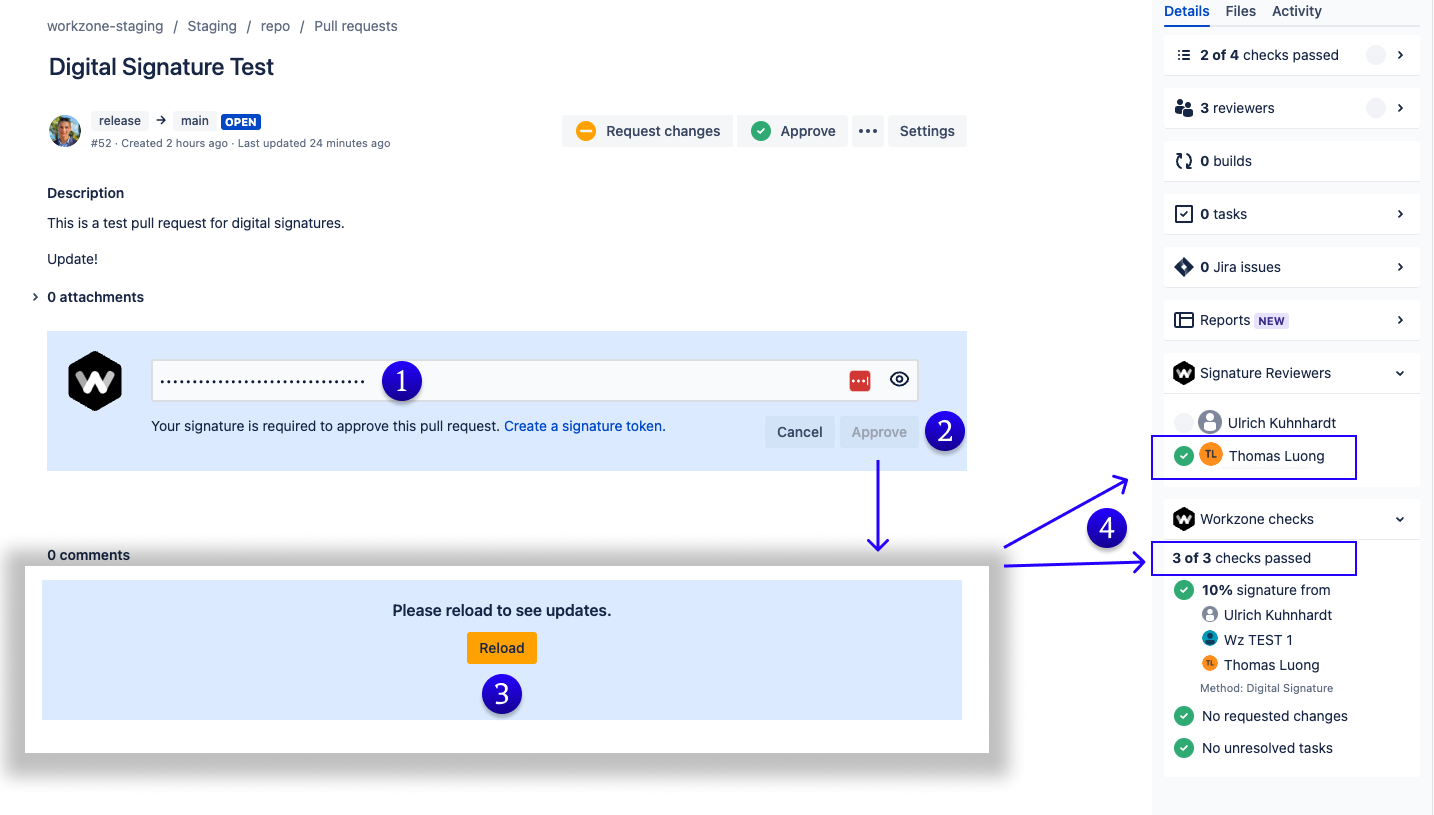
Not every team needs that. But for certain regulated or high-risk development processes, an explicit and traceable approval can be more appropriate than a normal lightweight code-review approval.
The principle is simple:
Automate what can be reliably automated, and make human judgment load-bearing where human accountability is required.
How Izymes Uses Workzone in Its Own Development Process
This is not only a workflow we recommend to customers.
Izymes uses Workzone within our own software development lifecycle.
Our published Security Practices describe a development process in which work is tracked, changes are submitted through Bitbucket Cloud pull requests, and Workzone adds reviewers and groups based on the pull request changes.
The configured reviewers must satisfy the applicable approval quota, while an automated vulnerability check provides another machine-enforced control. Once the required approval and security conditions have been met, Workzone can complete the merge.
This illustrates an important point about human-in-the-loop development:
The strongest model is not humans manually performing every check.
It is a system where automated checks and human accountability reinforce each other, and where the workflow consistently enforces the rules the organisation has decided matter.
Bitbucket CODEOWNERS vs Workzone
Bitbucket Cloud already provides useful native controls, so it is important to understand where Workzone adds additional functionality.
Bitbucket Cloud CODEOWNERS uses a .bitbucket/CODEOWNERS file to automatically select reviewers based on the files and directories changed in a pull request.
Separately, Bitbucket’s native merge checks can require conditions such as minimum approval counts. On Bitbucket Premium, unresolved merge checks can be configured to block merging.
For many teams, that may be enough.
The difference becomes important when the ownership rule and the approval requirement need to follow the particular files or modules being changed.
| Requirement | Bitbucket Cloud native | Workzone |
|---|---|---|
| Automatically add reviewers based on changed files/paths | Yes, with CODEOWNERS | Yes |
| Use individuals or teams/groups as reviewers | Yes | Yes |
| Require a general minimum number of approvals | Yes; blocking enforcement requires the appropriate Bitbucket plan/configuration | Yes |
| Associate an explicit approval quota with a particular file/module reviewer rule | Not through CODEOWNERS alone | Yes |
| Exclude contributor approvals from a path-specific Workzone quota | Not a CODEOWNERS rule | Yes |
| Require Workzone digital signatures as part of the approval workflow | No native equivalent | Yes |
Bitbucket Cloud also supports custom merge checks, giving teams another option for extending Bitbucket’s native merge process.
So the question is not:
Can Bitbucket enforce approvals?
It can.
The better question is:
Does our review policy need specific ownership and approval requirements to follow the branches, files or modules being changed?
That is where Workzone can provide more granular control.
For a deeper feature-by-feature comparison, see Workzone Cloud vs Bitbucket Cloud CODEOWNERS.
When You May Not Need Workzone
Not every Bitbucket team needs additional workflow tooling.
If your team has a relatively straightforward review process and Bitbucket CODEOWNERS plus native merge checks already provide the controls you require, keeping the workflow simple may be the right choice.
Workzone becomes more relevant when you need combinations such as:
- file or module-specific reviewer rules;
- explicit approval quotas for those rules;
- mandatory reviewer users or groups;
- different review requirements across branches or areas of the repository;
- independent-review requirements;
- digitally signed approvals;
- more detailed control over reviewer assignment and merge policy.
The objective should never be to add process for the sake of process.
It should be to make the minimum level of governance your organisation actually needs consistently enforceable.
The Human in the Loop Is a Design Choice
AI will continue to become more deeply involved in software development.
That does not mean every AI-assisted pull request should require exhaustive manual review. Nor does it mean automated systems should be allowed to write, review and ship high-risk changes without accountable human oversight.
Teams need to decide deliberately where humans remain load-bearing.
Let automation handle the checks it performs reliably. Identify the parts of the codebase where mistakes carry the greatest consequences. Then make sure the people responsible for those areas remain a required part of the merge decision.
If your goal is to protect critical code in Bitbucket, the most useful question is not whether humans or AI should do the reviewing. It is which checks should be automated, which decisions require accountable human approval, and how those rules are consistently enforced.
Because the teams that benefit most from AI-assisted development may not be the teams that simply generate the most code.
They will be the teams that can still confidently stand behind what they merge.
Want to enforce more granular reviewer and approval rules in Bitbucket?
Explore Workzone’s reviewer and approval configuration to see how file and module-based reviewer rules, approval quotas and independent-review controls can be incorporated into your pull request workflow.
If Bitbucket’s native CODEOWNERS and merge checks already meet your requirements, keep your workflow simple. If you need more granular control over who must review specific areas of your codebase, try Workzone for Bitbucket on the Atlassian Marketplace.
Last updated: August 2026